No matter the industry, running a business is an expensive undertaking. After operating costs are factored in, there often aren’t enough resources to pursue every new investment opportunity, so decision-makers want to see a clear path towards benefits before approving a new expenditure.
In these budget conversations, cybersecurity initiatives are often classified as static overhead costs, usually leading executives to provide an unchanging level of resources in each budget cycle to keep the department running. This can be frustrating to security personnel who want to pursue helpful initiatives, equipment, or security tests, but don’t get the same resources as other departments because they aren’t seen as profit drivers.
Changing this mindset, however, opens up a new form of brand investment that many companies haven’t yet considered. An actively supported cybersecurity department can make reliability, security, and consistent uptime into pillars of their brand’s identity, rather than a background trait to be taken for granted. This piece will walk through some methods of active cybersecurity investment, helping your company direct assets in a new direction and reap the benefits of dedicated digital protection.
Focus on Critical Systems
Thankfully, adopting an investment-forward view of cybersecurity doesn’t require a complete overhaul of every digital aspect of a business. Attempting to reimagine every information system from the ground up would likely result in a deficit of resources for any one initiative, so it’s important to prioritize.
Instead, companies can begin by determining which sides of their digital operations are most important or most in need of security updates. Analyzing the most important aspects of a business’ digital systems shows where assets can be centralized to achieve the most impact, achieving maximum returns with the most efficient investments.
Focusing on core business functions also eases the process of obtaining funding, as decision-makers have an easier time understanding the importance of protecting these priority systems. Because initiatives centered around priority systems justify themselves, they can be a good first step for changing the executive mindset around cybersecurity with quantifiable improvements.
Strengthen the Human Element
Improving digital controls is always a beneficial use of assets, but the most effective cybersecurity plans also account for personnel training. Cybersecurity threats can take a wide range of forms, and many of these attack strategies use social engineering or other employee-based tactics to gain system access.
Therefore, increasing staff threat awareness and security knowledge is a security initiative that some infosec teams fail to consider. Strengthening users to the same degree as the systems they use creates a digital ecosystem that’s less vulnerable to threats on both sides.
Catch Threats As They Arise
Traditional cybersecurity approaches often involve passive threat monitoring systems that can detect intrusions after they occur, but this strategy has been outpaced by the aggressive nature of modern cyberattacks. Implementing active monitoring solutions like endpoint detection can reduce the gap between intrusion and detection.
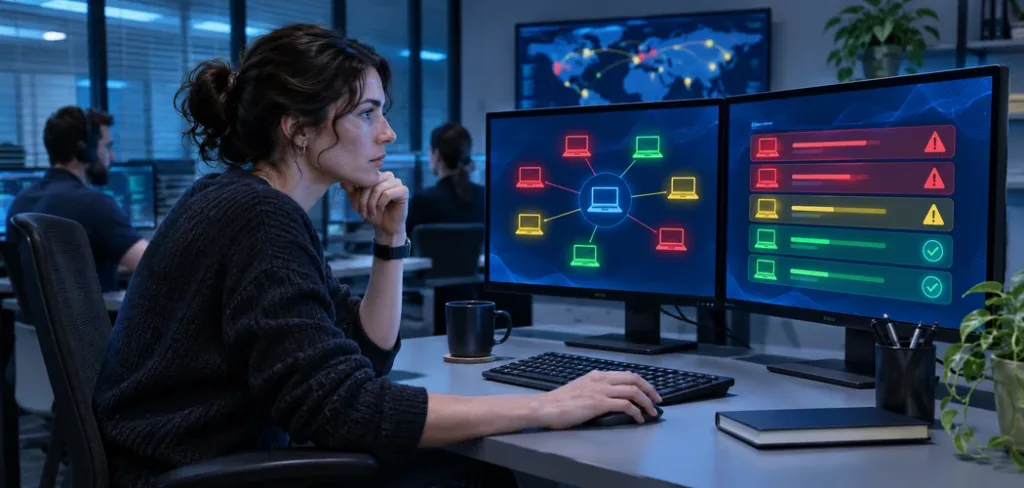
Active monitoring systems increase responsiveness in moments where every second matters. Taking a vigilant, active approach to threat monitoring is a great way to ward off threats in their earliest stages, further cementing reliability and security as brand identity pillars.
Utilize Trusted Security Standards
In addition to providing a helpful blueprint for effective cybersecurity readiness, security frameworks like HITRUST and CMMC demonstrate to external bodies that a company is intentional about its security planning. Collaborating with certified consultants and partners is also an effective way to increase cybersecurity readiness.
Implementing a security framework also helps to reduce confusion and increase efficiency in security operations. Using a framework as a primary source of truth makes it easier to locate best practices and keep guidelines unified, reducing variability across systems and decreasing overall vulnerability.
Create Data Backups and Disaster Plans
While there are several steps that cybersecurity teams can take to strengthen their company’s systems, it will never be possible to achieve complete invulnerability. Security controls are important, but intruder tactics and tools are always evolving, and it’s simply not feasible to plan for every possible weak point.
Because of this, it’s important for assets to be allocated towards creating data backups and disaster response plans. A security posture that accounts for both prevention and response allows a company to bounce back faster from a potential incursion, ultimately improving operational efficiency in the face of a major business disruption.
It’s also important to remember that these disruptions can have a variety of root causes, even outside of cyberattacks. While digital intrusions account for the majority of data loss, similar effects could also be brought about by natural disasters, fire, internal error, or a number of other issues. Creating backups not only guards against ransomware, but also helps companies get back up and running, no matter the cause of the setback.
Regularly Test Systems
The best way to determine the impact of any cybersecurity investment is to conduct regular testing. Third-party testing ensures that a given security control is functioning as intended, reveals unseen weaknesses, and can assess how a system stands up to an emerging threat. Testing can also be conducted on personnel, through strategies such as simulated phishing.
Penetration testing, in which a third-party consultant thoroughly inspects a digital system and documents its weaknesses, is one of the most effective and trusted methods for testing security controls. Inspectors will attempt to gain access to a targeted system over a given period of time, and will return a detailed report of their findings to clients. Most consultants will also offer guidance on remediating vulnerabilities, with testing often resuming until the client and tester are both satisfied.
Security Investments Safeguard Brand Consistency
While it’s easy for executives to view cybersecurity as a passive operating expense, there are many benefits to actively investing in security controls and tests. Keeping ahead of emerging threats and proactively improving security systems makes a company much less likely to experience major downtime during an intrusion.
Cybersecurity can also serve as an effective growth driver when given proper investment. Companies that handle customer or partner data will gain business when focusing on security, as clients will place more trust in a company with a proven track record for infosec readiness. Cybersecurity and IT investments reduce downtime from all sources, making it easier for all other departments to operate consistently.
Ultimately, by safeguarding critical systems, creating backups, and training personnel, cybersecurity teams can make their companies more reliable and resilient, enabling the organization to reach its long-term goals with a solid digital foundation.