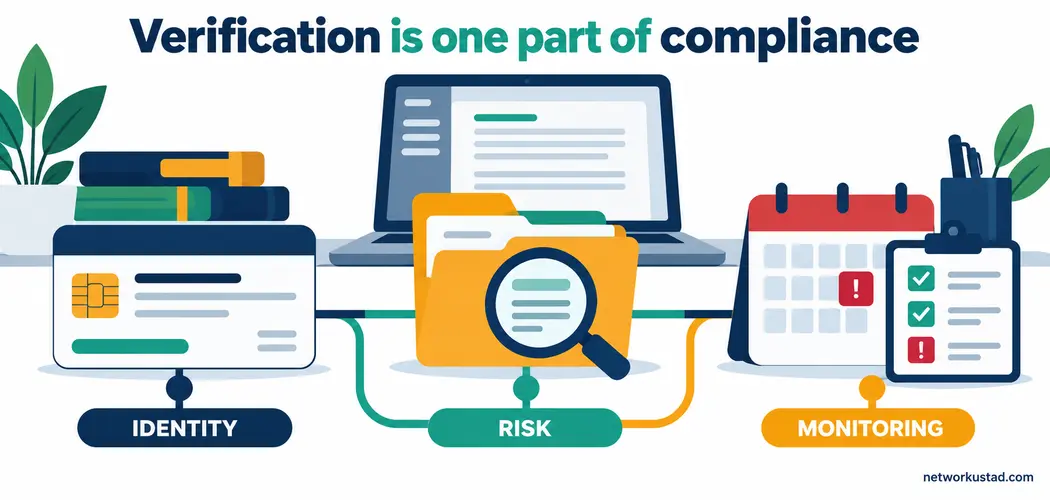
KYC and AML compliance involves more than collecting an identity document or buying verification software. A business needs to understand which obligations apply, what risks it faces, who makes decisions, and how concerns are reviewed. Technology can support those responsibilities, but it cannot turn an incomplete process into a compliant one by itself.
The distinction matters when a customer passes an ID check but other questions remain. Is the account being opened for a company? Who ultimately owns or controls it? Does the intended activity make sense for the relationship? Has something changed since the original information was collected?
This guide explains how the main concepts fit together without prescribing one universal workflow. It is general educational information, not a legal opinion for a particular business. Use the framework to ask better questions of your compliance team, advisers, and technology providers, then apply the rules and approved procedures relevant to your circumstances.
What KYC and AML compliance actually covers
Know Your Customer, or KYC, is commonly used as an umbrella term for understanding and checking customers. In practice, people use the term differently, so an organization’s procedures should define what each check is intended to establish.
Anti-money laundering, or AML, concerns measures intended to prevent, detect, and respond to money laundering. Related frameworks also address terrorist financing and other financial-crime risks. The exact requirements and terminology depend on the legal system and the activity involved.
Customer due diligence, or CDD, includes identifying and verifying customers and other applicable measures for understanding and reviewing a relationship. It should not be described as something that begins only after onboarding. Equally, ongoing monitoring should not be reduced to repeating an ID scan at fixed intervals.
The FATF Recommendations set international standards that countries implement through their national frameworks. FATF is not the authority that directly fines every business for an unsuccessful customer check. Establish which domestic rules, regulators, and supervisory arrangements apply to your organization.
Do not assume that all online sellers have the same obligations as banks or other regulated financial businesses. Selling over the internet is not, by itself, enough information to determine an organization’s complete AML duties.
Start with scope, responsibilities, and a usable risk assessment
Before selecting software, identify the business activity, customer types, products, delivery channels, and jurisdictions involved. These details shape what information is needed and which decisions require specialist input.
Assign responsibility for the process. Staff should know who owns the policy, who reviews exceptions, who can approve a relationship, and who handles potential reporting obligations. A clear escalation route is more useful than a dashboard containing alerts that nobody is accountable for resolving.
A practical risk assessment should explain why a concern matters and what response is proportionate. It should also identify the limits of the available evidence. A single signal, such as an unfamiliar address or a device location, may have an innocent explanation and should not silently become a conclusion.
For KYC and AML compliance, distinguish the organization’s assessment from a vendor’s score. A numerical result may help prioritize work, but the business needs to understand what the score represents, what it omits, and how it affects a decision.
Document how policy changes are approved and communicated. If an obligation or risk changes, update the relevant controls, training, and review process together. Changing a rule in software without explaining it to the people who act on the results can create inconsistent decisions.
Separate identity proofing from account authentication
Identity proofing aims to establish a relationship between an applicant and a real-world identity to an appropriate level of assurance. Authentication concerns demonstrating control of an authenticator associated with an account. They solve different problems.
Two-factor authentication can strengthen account access, but receiving a code does not automatically establish someone’s legal name, beneficial ownership, or the validity of an identity document. A person may control a phone or account without having completed the required identity checks.
NIST’s identity-proofing guidance distinguishes resolving an identity, validating evidence and attributes, and verifying the applicant’s association with them. Its assurance-based approach is more useful than treating a document upload, selfie, and text message as a universal recipe.
Where documents are used, establish what the check can assess. Reading text through optical character recognition extracts information; it does not independently prove that the document is genuine. A plausible document template is also not the same as a confirmed relationship between the presenter and the identity.
Biometric comparison and presentation-attack detection have different functions. Comparing a face with a reference photograph is not identical to assessing whether a capture appears live. Neither feature should be described as eliminating every impersonation or injection threat.
The appropriate combination depends on the service and applicable requirements. Offer review and accessible alternatives where appropriate, rather than assuming every unsuccessful automated result represents attempted fraud. For more background, see NetworkUstad’s explanation of online ID verification.
Understand the customer relationship, not just the document
An ID check addresses one part of KYC and AML compliance. The relationship may require additional information about the customer, the reason for using the service, expected activity, and relevant ownership or control.
For a company, verifying the employee who completes a form does not necessarily answer who owns or controls the customer. Establish what the applicable framework requires you to understand about legal entities and beneficial owners. Avoid copying a threshold from another jurisdiction without checking whether it applies.
Keep questions relevant to the purpose of the relationship and the applicable risk. Collecting every available document is not automatically a stronger process. Unnecessary collection increases the burden on customers and creates more information to protect, maintain, and eventually dispose of appropriately.
Where further information about funds or wealth is required, explain what question needs to be answered and what evidence is appropriate. Do not treat those terms as interchangeable or assume that every customer needs the same investigation.
Record unresolved issues and the basis for decisions. An approval should be understandable to a later reviewer without depending on the original employee’s memory. If an exception is permitted, document who authorized it and what follow-up is needed under the approved procedure.
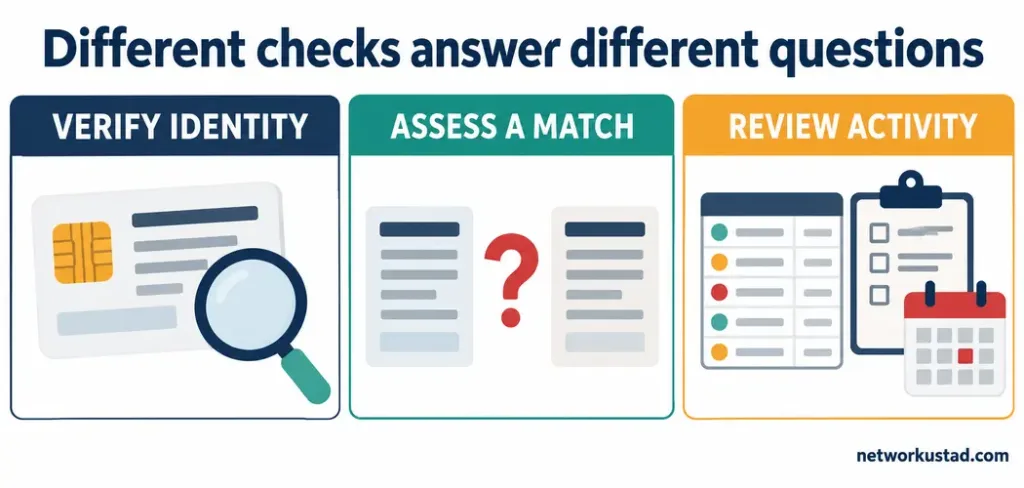
Screening and monitoring answer different questions
Screening may compare customer information against sanctions lists, politically exposed person information, or other relevant sources. Monitoring considers activity and changes over the relationship. Neither is simply another name for checking an ID document.
A possible screening match needs assessment. Similar names, incomplete records, transliteration, and outdated information can create ambiguity. A list result should not automatically be treated as proof that two records describe the same person.
Politically exposed person status is a risk-management consideration, not an accusation of criminal conduct. Sanctions restrictions, PEP measures, and other risk indicators must not be collapsed into one generic category of a prohibited customer. Apply the relevant rules and escalation process to each issue.
Monitoring also requires context. An unusual transaction may justify review, but unusual does not necessarily mean unlawful. Staff need to understand the concern, the available explanation, and what information or action is appropriate next.
For KYC and AML compliance, define what happens after a concern is raised. Assign a reviewer, protect relevant records, document the reasoning, and follow the applicable rules for handling the matter. Do not equate closing an alert in a system with resolving the underlying risk.
Where a reporting decision may be required, use the designated function and current procedures. Reporting obligations and restrictions on disclosure are jurisdiction-specific; an employee should not improvise them from a general internet article.
Use automation with evidence and accountable oversight
Automation can assist with document handling, matching, prioritization, and other repetitive tasks. Its value should be demonstrated for the actual use case, rather than inferred from an AI label.
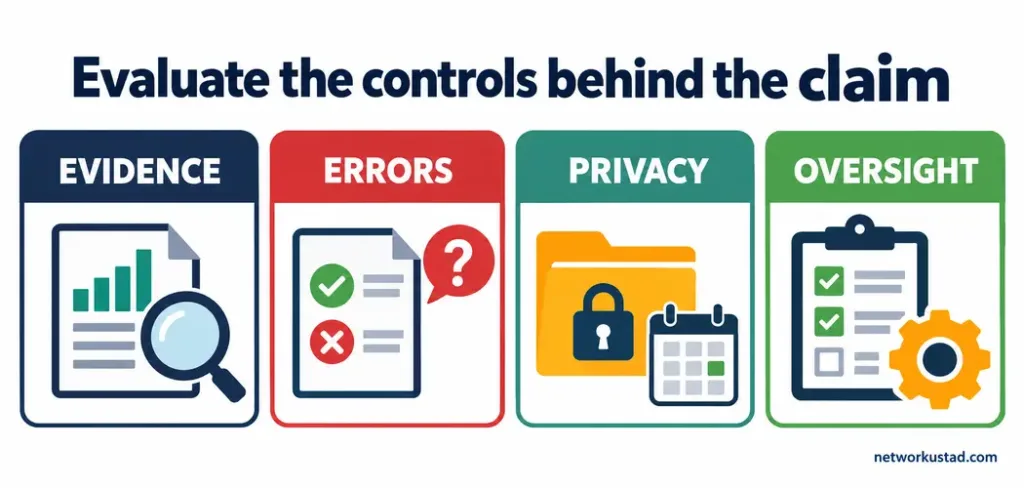
Ask what a claimed accuracy percentage measures. Is it document classification, face comparison, detection of a particular attack, or the outcome of a complete workflow? Results from different tasks cannot be compared as though they describe the same thing.
Examine the test population, conditions, and error definitions. A low false-positive rate may be achieved at the cost of missing more genuine concerns. A result from a controlled demonstration may not describe customers using older devices, poor connections, or documents from different countries.
Assess KYC and AML compliance tools against your own requirements and representative scenarios. Include ordinary successful cases, legitimate customers who encounter difficulties, and the threats relevant to the service. Decide who reviews results and what evidence would justify changing a threshold.
Do not accept blanket claims that blockchain, federated learning, or a privacy-preserving technique guarantees compliance. Each has a particular design and scope. Determine what data is processed, which parties can access it, and which obligations remain with the business.
An automated recommendation should have a defined place in the decision process. Staff need enough information to understand the issue, challenge an apparent error, and escalate appropriately. Human involvement is useful only when reviewers have the time, training, authority, and evidence to perform that role.
Protect customer information in KYC and AML compliance
KYC and AML compliance can involve sensitive identity and financial information. Decide what needs to be collected, where it is stored, who can access it, and how it is protected during transfer and use.
Retention should follow applicable obligations and an approved schedule. Do not promise immediate deletion of every record if the business must retain some information. Equally, avoid keeping everything indefinitely simply because storage is available.
For an external provider, examine the actual arrangement. Identify subprocessors where relevant, hosting locations, permitted uses, access controls, incident responsibilities, and the return or deletion process when the contract ends. A general statement that a product is secure is not a substitute for those details.
Prepare for errors as well as attacks. A customer may need to correct information, request review, or use another supported route. Make the process understandable without disclosing details that could compromise controls or breach legal restrictions.
Keep investigation and identity information out of unapproved public tools. Staff should know which systems are authorized and how to seek help when a document or activity record is difficult to interpret. Convenience is not a sufficient reason to share a customer’s data elsewhere.
Evaluate providers beyond the sales demonstration
When evaluating KYC and AML compliance software, bring a written requirements list to the discussion. Separate essential functions from features that are attractive but unnecessary for your current service.
Ask the provider to explain:
- Which tasks the product performs and which remain with your organization.
- What evidence supports its performance claims and where limitations are known.
- How unsuccessful checks, ambiguous matches, and customer appeals are handled.
- How changes to models, data sources, or matching rules are communicated.
- What records are available for reviewing a decision later.
- How data access, retention, security incidents, and contract exit are managed.
Check the operating costs too. Include implementation, integration, usage, manual review, training, support, and any work needed when the service changes. A low per-check price may not describe the complete cost of running the process.
Use a pilot with agreed evaluation criteria where appropriate. Record the conditions and limitations of the exercise. Do not present a small internal trial as independent proof that the product performs equally well for every customer or threat.
Finally, identify who can approve deployment and what would trigger reassessment. A successful launch does not remove the need to review errors, emerging risks, policy changes, and provider performance.
KYC and AML compliance needs training and review
An effective process needs people who can interpret the information in front of them. Train staff for their actual responsibilities, including what they can decide and what must be escalated.
Use realistic, appropriately anonymized exercises. Test whether staff can distinguish an identity issue from a screening concern, explain missing information, and produce a clear case note. Avoid judging learning only by whether a short quiz was completed.
NetworkUstad’s guide to choosing AML training explains how to compare learning objectives, assessment, eligibility, and total cost. A qualification can support development, but it does not replace the organization’s own procedures or the experience required for a role.
Review KYC and AML compliance through more than one metric. Processing speed, error patterns, unresolved cases, customer difficulties, and the quality of decisions all matter. A faster process is not automatically a safer or more appropriate one.
Keep a record of issues found and the actions taken. Assign owners and follow up. Where a policy, training gap, or software setting repeatedly causes problems, address the cause rather than treating every case as an isolated mistake.
Frequently asked questions about KYC and AML compliance
Is KYC the same as AML?
No. KYC concerns knowing and checking customers, while AML covers a broader framework for addressing money-laundering risk. Customer due diligence connects identification with other applicable measures for understanding and reviewing a relationship. Define the terms clearly in your own procedures.
Does every online seller need the same checks?
No. Obligations depend on the business activity, jurisdiction, customer, and other relevant circumstances. Do not assume that operating a website creates the same duties as a regulated financial institution. Establish the applicable scope before copying another business’s process.
Does passing an ID check establish compliance?
No. It addresses a particular question within a broader process. Other issues may include ownership, the purpose of the relationship, applicable screening, ongoing activity, recordkeeping, and the handling of concerns. Required measures depend on the framework that applies.
Are biometrics and AI always mandatory?
No universal requirement follows from the terms KYC or AML. Appropriate methods depend on applicable rules and the risk and assurance requirements of the service. A technology provider’s recommendation is not, by itself, a legal mandate.
Does a screening match prove wrongdoing?
No. Establish whether the information actually matches the customer and what the relevant finding means. PEP status is not an accusation of crime, and sanctions issues require their own applicable assessment and action. Follow approved procedures rather than relying on a name match alone.
What should a business do first?
Confirm which obligations and risks apply, assign responsible people, and document the decisions the process must support. Then evaluate information needs, controls, technology, training, and review arrangements against that scope. Seek qualified advice for the specific legal questions involved.