Ask a working penetration tester, SOC analyst, or malware researcher which programming language shows up most often in their daily toolkit, and Python comes up more than any other. It isn’t the only language security professionals use, and it isn’t always the fastest option — but its combination of a huge library ecosystem, fast prototyping speed, and a genuinely low barrier to entry has made it the default scripting language across nearly every corner of the security field.
This guide covers why that is, what Python actually does well (and where it doesn’t), the libraries that come up most in real security work, and what the current threat landscape looks like in terms that are actually sourced, not just quoted.
The Scale of the Problem Python Is Being Used to Fight
It’s worth grounding this in real, current numbers rather than the kind of unsourced statistic that circulates in too many “cybersecurity 101” articles. IBM’s 2025 Cost of a Data Breach Report — based on a survey of 600 breached organizations — found the global average cost of a data breach was $4.44 million, which was actually the first year-over-year decline in five years. In the United States specifically, the average cost hit a record $10.22 million, driven largely by regulatory fines and detection costs.
A few other figures from that same report are worth knowing, because they shape what security teams actually spend their time on: 76% of organizations took longer than 100 days to fully recover from a breach, and only 2% recovered in under 50 days. Phishing was the single most common initial attack vector, responsible for 16% of breaches, while insider attacks — though less common — were the costliest initial vector at an average of $4.92 million per incident. Ransomware victims are also increasingly refusing to pay: 63% of organizations declined to pay a ransom in 2025, up from 59% the year before.
These numbers matter for a Python-and-security article specifically because they explain the shape of the work: detection, response, and automation at scale, under real time pressure — exactly the kind of work scripting languages are built to support.
Why Python Specifically
A few concrete properties explain Python’s dominance in this field, beyond “it’s popular”:
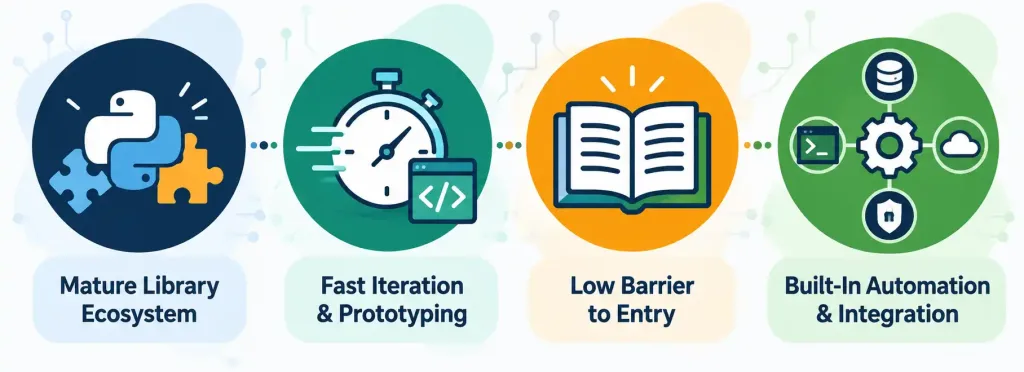
- A mature security-specific library ecosystem. Nearly every common security task — packet manipulation, protocol interaction, cryptography, web request automation — already has a well-maintained Python library behind it, which means security engineers are rarely starting from scratch.
- Fast iteration for one-off and custom tooling. A lot of security work involves writing a script once, for one specific target or one specific investigation, rather than building production software. Python’s quick write-test-run cycle fits that workflow better than a compiled language typically does.
- Readable syntax that lowers the barrier for cross-functional teams. Security work increasingly involves people without a traditional software engineering background — threat intelligence analysts, incident responders, compliance staff writing automation for their own workflows. Python’s relatively gentle learning curve makes it realistic for that broader group to contribute scripts and tooling, not just dedicated developers.
- First-class support for automation and integration. Security operations centers lean heavily on automating repetitive tasks (log parsing, alert triage, indicator-of-compromise checking across multiple feeds), and Python’s standard library plus its ecosystem of API clients make that kind of integration work straightforward.
None of this makes Python strictly “better” than every alternative in every situation — C and Rust remain relevant for performance-critical tooling and exploit development at a low level, and Bash remains the default for quick system-administration one-liners. Python’s advantage is breadth: it’s good enough, with enough library support, across more of the field than any single competitor.
A useful way to frame the comparison: Bash is usually faster to reach for when the task is a quick, single-system administrative action, like searching through log files already on a machine you’re logged into. C and Rust earn their place when performance or memory-level control genuinely matters, such as building an exploit that depends on precise control over memory layout. Python sits in the space between those two extremes — expressive enough to build real tooling quickly, with enough low-level library access (through things like Scapy and Socket) to still reach into packets and protocols directly when needed, without the development overhead a compiled language adds for a one-off script.
Python Libraries That Actually Show Up in Security Work
Rather than a generic list, here’s what these libraries are actually for, since getting this wrong matters when readers are deciding what to learn:
- Scapy — a packet manipulation library capable of forging, decoding, sending, and capturing network packets, and matching requests to their replies. It can effectively replicate functionality found in tools like Nmap, Wireshark, hping, and tcpdump from within a Python script, and it’s commonly used for custom network reconnaissance and protocol fuzzing.
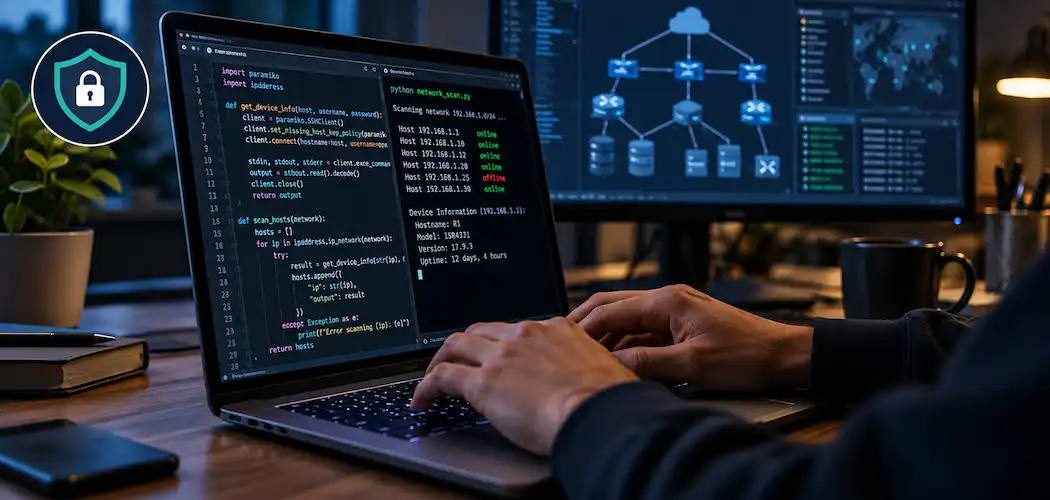
- python-nmap — a wrapper that lets a script run Nmap scans and parse the structured results programmatically, useful for building custom scanning workflows or feeding scan results into other automated tooling.
- Impacket — a collection of classes for working directly with network protocols, especially Windows protocols like SMB, MSSQL, and DCERPC. It’s widely used for Windows-environment reconnaissance, authentication testing (including hash-based authentication), and exploit development.
- Requests — a library for sending HTTP requests from a script, commonly used to automate custom payloads and test web application behavior in ways that off-the-shelf tools like Burp Suite don’t cover out of the box.
- BeautifulSoup — an HTML and XML parsing library, typically paired with Requests to extract specific data out of web responses. It’s a parsing tool, not a network-scanning tool, despite sometimes being miscategorized that way.
- Socket — Python’s low-level networking library, the foundation that many higher-level security tools (including some of the ones above) are themselves built on. Understanding it directly is useful for building custom client/server tooling.
- PyCryptodome — a maintained, actively developed cryptography library for tasks like hashing, encryption, and digital signatures. It’s worth noting specifically that its predecessor, PyCrypto, has been unmaintained for years and shouldn’t be used in new projects — PyCryptodome is its drop-in, maintained successor.
Where Python Fits in a Security Career
Python shows up across nearly every security specialization, though the specific skills that matter differ by role:
- Penetration testing and red teaming: writing custom exploits, automating reconnaissance, and building tooling around the libraries above when existing tools don’t fit a specific target.
- Malware analysis: scripting static and dynamic analysis workflows, automating the extraction of indicators of compromise from samples, and building custom sandboxing or unpacking tools.
- Security operations and incident response: automating log parsing and correlation, building custom alert-triage scripts, and integrating disparate security tools that don’t natively talk to each other.
- Security research and tool development: building entirely new security tools, from vulnerability scanners to custom fuzzers, where Python’s rapid prototyping speed shortens the path from idea to working proof of concept.
A Practical Starting Point for Learning
For someone starting from general Python fluency and wanting to move into security-specific scripting, a reasonable progression looks like this:
- Get comfortable with core Python first — data structures, file handling, and working with external libraries via pip — before layering security-specific tools on top. Security scripting is still just Python; the libraries are the specialized part, not the language itself.
- Start with Requests and BeautifulSoup for basic web automation and data extraction, since these come up constantly and have a gentle learning curve compared to lower-level networking libraries.
- Move to Scapy once comfortable with networking fundamentals (how packets, ports, and protocols actually work) — Scapy is powerful but far more useful once you understand what you’re asking it to build or inspect.
- Learn Impacket when working specifically in Windows-heavy environments, since its value is tightly tied to understanding the Windows protocols it wraps (SMB, DCERPC, and similar).
- Practice in a legal, controlled environment. Deliberately vulnerable practice platforms and personal lab environments exist specifically so this kind of scripting can be learned and tested without touching systems you don’t have explicit permission to test — running these tools against anything else is both unethical and, in most jurisdictions, illegal.
A Note on Scope: Automation Doesn’t Replace Understanding
It’s worth being direct about a common misconception: learning to run existing Python security tools and scripts is not the same as understanding the underlying security concepts those tools automate. A script that runs an Nmap scan via python-nmap is only useful to someone who already understands what a port scan is telling them; a script built on Impacket for Windows authentication testing is only safely usable by someone who understands the authentication mechanisms it’s interacting with.
Python tooling multiplies the effectiveness of security knowledge someone already has — it doesn’t substitute for that knowledge. Treating libraries as a shortcut around learning networking, operating systems, and protocol fundamentals tends to produce scripts that work in a tutorial but fail (or cause real damage) against an unfamiliar real-world target.
The Bottom Line
Python’s position in cybersecurity isn’t hype — it’s a direct result of its library ecosystem, its speed for building and iterating on custom tooling, and the breadth of people it makes security scripting accessible to. Learning it well means going beyond “Python is popular” and actually understanding what specific libraries do (Scapy for packets, Impacket for Windows protocols, Requests and BeautifulSoup for web work, PyCryptodome for cryptography), since using the wrong tool — or an abandoned one, like the old PyCrypto library — can cost real time and introduce real risk in work where precision matters.
Frequently Asked Questions
Is Python the best language for cybersecurity?
It’s not the only language that matters — C and Rust remain important for performance-critical and low-level work, and Bash is still the default for quick system tasks — but Python’s combination of library support, fast iteration, and accessibility makes it the most broadly useful language across the widest range of security specializations.
What’s the difference between PyCrypto and PyCryptodome?
PyCrypto is an older cryptography library that has been unmaintained for years and should not be used in new projects. PyCryptodome is its actively maintained, drop-in successor and is the one to use for any current Python cryptography work.
Is BeautifulSoup used for network scanning?
No — BeautifulSoup is an HTML and XML parsing library, typically used alongside the Requests library to extract specific data from web page content. Actual network scanning is typically handled by libraries like Scapy or python-nmap.
How much does a data breach actually cost on average?
According to IBM’s 2025 Cost of a Data Breach Report, the global average was $4.44 million — the first year-over-year decline in five years — while the U.S. average hit a record $10.22 million, driven largely by regulatory fines and detection costs.
Do I need a computer science degree to use Python for security work?
No. Python’s relatively gentle learning curve is part of why it’s become so central to the field — it’s realistic for analysts, incident responders, and other security professionals without a traditional software engineering background to learn enough to write useful automation and tooling.
Is it legal to practice Python security scripts against real websites?
No, not without explicit authorization. Running reconnaissance, scanning, or exploitation scripts against systems you don’t own or have written permission to test is illegal in most jurisdictions, regardless of intent. Practice should happen against dedicated, deliberately vulnerable lab environments built for that purpose, or systems you own and control directly.
Can learning Python security libraries substitute for learning networking and security fundamentals?
No — the libraries automate tasks, but interpreting their output and applying them safely and effectively still depends on understanding what’s actually happening underneath: how ports and protocols work, how authentication mechanisms function, and what a scan or packet capture is actually revealing. Treating the tooling as a shortcut around that foundational knowledge tends to produce scripts that work in a tutorial but fail against a real target.