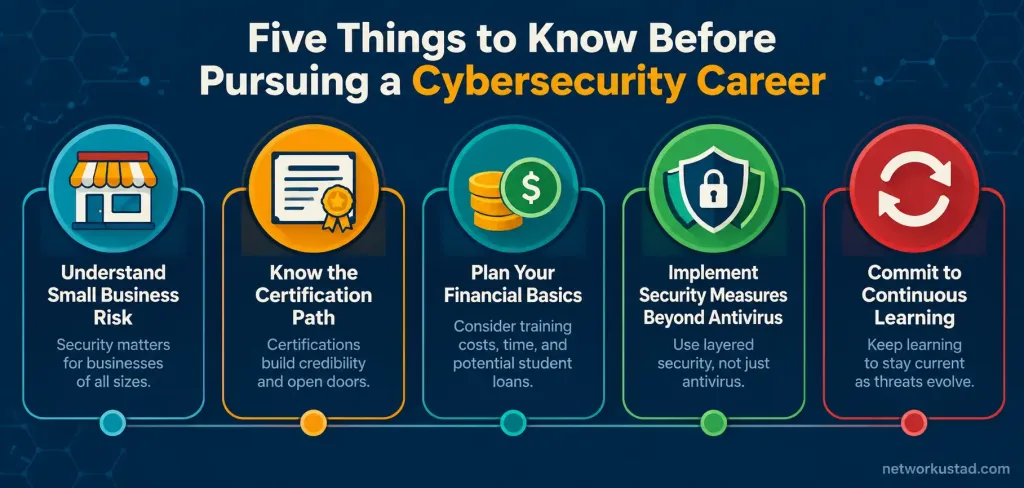
Cybersecurity sounds like one job. It isn’t. The field covers dozens of specialties, from threat hunting to compliance auditing to cloud architecture, and the day-to-day work varies enormously depending on which corner you end up in. That variety is part of why “what do cybersecurity people actually do” is a harder question to answer than it looks — a bit like describing what doctors do in two sentences. Before committing time and money to a career in cybersecurity, or hiring someone who claims expertise in it, these five things are worth knowing.
Why This Field Is Worth a Serious Look Right Now
The numbers back up the hype, for once. The U.S. Bureau of Labor Statistics projects information security analyst roles to grow 21% from 2025 to 2035, far faster than the average occupation, with about 14,100 openings a year over that stretch. Median pay sits at $129,180 a year as of May 2025. That demand isn’t just about headcount, either. ISC2’s 2025 Cybersecurity Workforce Study found 59% of security teams report serious skills shortages, up sharply from 44% the year before, with AI security and cloud security topping the list of hardest-to-fill specialties. Put simply: there’s real, measurable room in this field for people who build the right skills.
What a Career in Cybersecurity Actually Covers
Before getting into the five specifics, it helps to be clear about scope. A career in cybersecurity isn’t one job title — it’s an umbrella covering threat hunters who chase active intrusions, compliance analysts who document controls for auditors, cloud security engineers who lock down infrastructure, and incident responders who clean up after a breach, among many other lanes. Someone considering a career in cybersecurity should expect to pick a lane eventually, even if entry-level work tends to touch a bit of everything.
1. Protection Isn’t Just for Big Companies
A common misconception among people new to a career in cybersecurity is that the work only matters for large enterprises. It doesn’t. Even one-person service businesses that run entirely online face the same identity-theft and ransomware exposure that bigger companies do, often with far fewer resources to recover if something goes wrong. A solo consultant storing client data in a cloud spreadsheet has real exposure, and so does a two-person online shop taking payments through a web form. Security professionals who understand this gap — and can scale their advice down to a small business’s actual budget — tend to be more useful than ones who only know how to talk to enterprise security teams.
2. You Don’t Need a Four-Year Degree to Start, But It Still Helps
Most working security professionals do hold degrees, often in computer science, information technology, or a related engineering field, and a degree remains the most direct path into certain roles — particularly government positions and senior architecture roles that explicitly require one. But the field has built a real alternative path that didn’t exist in the same form a decade ago: industry certifications. CompTIA Security+ is the standard entry-level credential and requires no college degree at all, just foundational knowledge of networking and security concepts. From there, certifications like CompTIA CySA+ (security analytics) or PenTest+ (penetration testing) let someone specialize without going back to school, and employer job postings increasingly list “Security+ or equivalent experience” rather than demanding a specific degree.
That doesn’t mean certifications and a degree do the same thing. A degree tends to open doors faster at larger, more traditional organizations and government agencies; certifications tend to get someone hired faster at smaller companies and in hands-on technical roles. Knowing which door you’re actually trying to walk through changes which path makes more sense.
3. If You Do Pursue a Degree, Get the Loan Order Right
This is worth correcting directly, because bad advice here costs real money for years. The smartest route for most students isn’t to default to a private lender — it’s to exhaust federal student loan options first, which generally requires filing the FAFSA. Federal loans carry fixed interest rates, don’t require a credit check for most undergraduate loans, and come with protections private lenders typically don’t offer: income-driven repayment plans that can lower payments based on earnings, deferment and forbearance options during hardship, and forgiveness programs like Public Service Loan Forgiveness. Private lenders can fill a genuine gap when federal borrowing limits fall short of actual costs — a dependent undergraduate can only borrow up to $31,000 total in federal loans — but treating a private loan as the default first choice skips protections that matter most for exactly the kind of financial uncertainty a new graduate is likely to face.
4. Antivirus and a Firewall Are the Beginning, Not the Whole Job
Most people know about antivirus software and basic firewalls. Professionals in the field build on top of those basics with less-visible layers: regular, tested data backups; continuous monitoring for unusual network activity; disciplined password and credential management, often through dedicated password managers and multi-factor authentication; and encryption applied to data both at rest and in transit. None of these tools work well in isolation. A backup that’s never tested for restoration is not a real backup, and monitoring tools that nobody reviews don’t catch much. Larger organizations often keep dedicated in-house teams to manage all of this continuously; smaller businesses usually rely on a managed security provider or a part-time consultant to cover the same ground at a lower cost.
5. The Field Changes Faster Than Almost Any Other Tech Specialty
New attack techniques, new regulatory requirements, and new defensive tools show up on a near-constant basis, which means a credential earned once isn’t a permanent qualification. Most certifications, including CompTIA’s and ISC2’s CISSP, require continuing education credits to stay active — typically renewed every one to three years through conferences, training, or additional coursework. ISC2’s own research found that AI security and cloud security are now the two most in-demand specialties, a shift from a few years ago when zero trust architecture and digital forensics dominated the conversation. Someone who stopped learning after their first certification is already behind; staying current isn’t optional in this field the way it might be in a more stable technical specialty.
Entry-Level, Mid-Career, and Senior: What Actually Matters at Each Stage
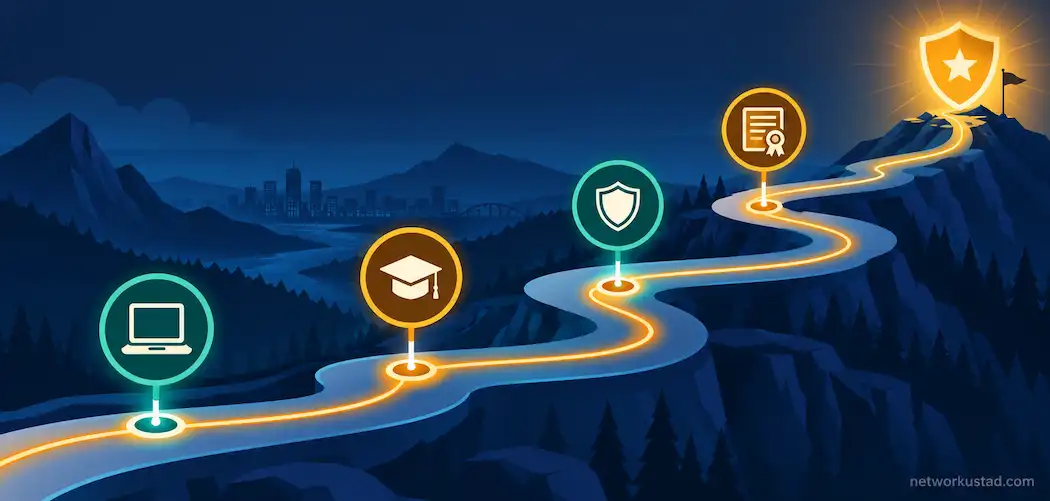
The certifications and experience that help most change depending on where someone is in a cybersecurity career, and conflating the stages is a common source of wasted time and money.
- Entry-level: CompTIA Security+ is the most widely recognized starting credential and the one most employers expect to see, even without a degree. Hands-on home-lab experience — setting up a firewall, running a vulnerability scanner, practicing basic incident response — matters more at this stage than a long list of certifications.
- Mid-career: Specialization starts to pay off. CySA+, PenTest+, or vendor-specific certifications (cloud platforms, SIEM tools) help someone move from general IT security work into a specific lane like threat detection, penetration testing, or cloud security — currently the two hottest specialties according to ISC2’s 2025 data.
- Senior/management: CISSP and CISM carry the most weight for leadership and architecture roles, and these typically require several years of verified professional experience before someone can sit the exam, not just study material.
Common Mistakes People Make Breaking Into Cybersecurity
A few patterns show up often enough to name directly. Collecting certifications without any hands-on practice is one of the most common — a stack of credentials with no home-lab experience, no personal projects, and no practical troubleshooting history reads as thin to hiring managers who’ve seen it before. Building even a small home lab, or contributing to open-source security tooling, demonstrates far more than another certification badge on a resume.
Defaulting to a four-year-degree-only mindset is another frequent misstep, especially now that certification-based entry paths are genuinely viable for many roles. And on the financial side, assuming a private student loan is the obvious or “smartest” choice, without first checking federal loan eligibility through the FAFAS, is a mistake that can cost thousands of dollars over the life of a loan in lost protections and higher rates.
The Bottom Line
A career in cybersecurity offers real, growing demand — 21% projected job growth, a median salary over $129,000, and a widening skills gap that favors people who build practical, current expertise. Getting there doesn’t require a single fixed path: a degree still opens certain doors fastest, but certifications like Security+ now offer a genuinely viable alternative route for many roles. Whichever path someone takes, getting the financial basics right — federal loans before private ones, if a degree is part of the plan — and committing to continuous learning once credentialed matter just as much as the initial certification or diploma itself. Anyone weighing a career in cybersecurity seriously is better served starting with one of the entry paths above than trying to prepare for all of them at once.
How Long It Actually Takes to Break In
A realistic timeline matters more than most career-change advice admits. Someone starting from scratch, with no IT background at all, typically spends six months to a year building foundational networking and systems knowledge before a Security+ certification makes sense to attempt. From there, landing a first role — often a help-desk or junior SOC analyst position rather than a specialist title — commonly takes another few months of applications, even with the credential in hand. People already working in general IT tend to move faster, sometimes transitioning into a security-focused role within the same company in well under a year, since they’ve already built the baseline technical literacy a career in cybersecurity requires. Expecting an instant transition, rather than this gradual on-ramp, is one of the more common sources of frustration for career changers.
Is It Worth Pursuing Right Now
Given the demand numbers and skills gap covered above, a career in cybersecurity is a reasonable bet for someone willing to put in genuine study time, not a guaranteed shortcut to a high salary. The field rewards people who can demonstrate real, current skill — a home lab, a certification backed by actual troubleshooting experience, familiarity with at least one cloud platform’s security tooling — over people who simply hold a credential and nothing else to show for it. For anyone weighing whether a career in cybersecurity fits their situation, the honest answer depends less on talent and more on willingness to keep learning past the first certification, since the field’s pace of change is itself one of the main things separating people who stay employable from people who stall out a few years in.
Frequently Asked Questions
Do I need a college degree to work in cybersecurity?
Not always. Certifications like CompTIA Security+ offer a genuine entry path without a degree, and many smaller companies and hands-on technical roles hire based on certification and demonstrated skill. Government positions and some senior architecture roles still typically require a degree.
What’s the first certification most people should get?
CompTIA Security+ is the standard entry-level credential most employers recognize, covering foundational networking and security concepts without requiring prior security work experience.
Is a cybersecurity career actually in demand right now?
Yes. The Bureau of Labor Statistics projects 21% job growth for information security analysts from 2025 to 2035, with about 14,100 openings per year, and ISC2’s 2025 Workforce Study found 59% of teams report serious skills shortages.
Should I use a private student loan to pay for a cybersecurity degree?
Only after exhausting federal loan options through the FAFSA. Federal loans offer fixed rates, income-driven repayment, deferment and forbearance, and forgiveness programs that private lenders generally don’t match. Private loans can fill a gap federal limits don’t cover, but shouldn’t be the default first choice.
What’s the difference between Security+ and CISSP?
Security+ is an entry-level credential with no required work experience. CISSP is a senior-level credential from ISC2 that requires several years of verified professional security experience before someone can even sit the exam, and it carries far more weight for management and architecture roles.