- How social engineering manipulates trust, urgency, authority, fear, curiosity, or helpfulness.
- How to distinguish phishing, spear phishing, whaling, vishing, and smishing.
- How business email compromise, impersonation, and pretexting work in real-world scenarios.
- How misinformation differs from disinformation.
- How watering-hole attacks, brand impersonation, and typosquatting target people and trusted online destinations.
- How to verify suspicious requests, protect credentials, report incidents, and reduce social-engineering risk.
- How to identify the most likely technique from Security+ scenario clues.
This lesson expands the human-based threat-vector and social-engineering techniques listed in Domain 2.0, Objective 2.2. It builds on Lesson 02.2 by explaining the attack methods, their distinguishing clues, and practical defenses.
What Is Social Engineering?
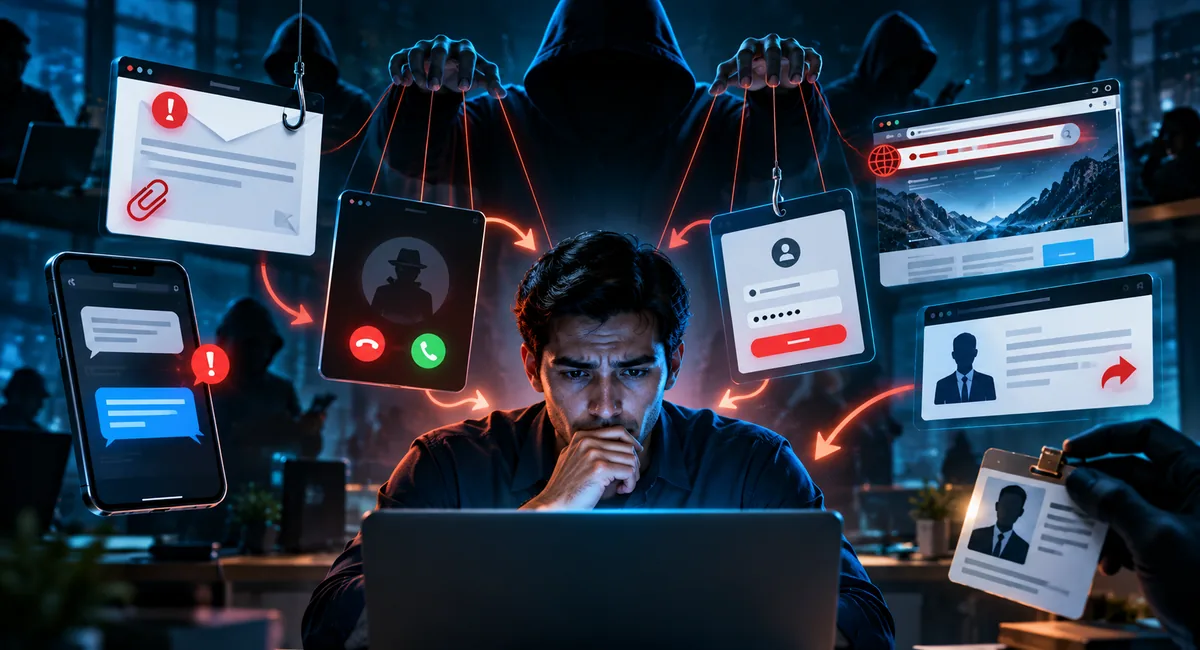
Social engineering is the use of deception or manipulation to persuade a person to reveal information, grant access, perform an unsafe action, or support a fraudulent activity. Instead of relying only on a technical weakness, the attacker targets human trust, decision-making, or normal business routines.
The attacker may pretend to be an executive, colleague, supplier, support technician, financial institution, delivery service, or another trusted party. A request might involve clicking a link, opening a file, sharing a one-time authentication code, approving a login, changing payment information, or allowing someone into a restricted area.
NIST describes social engineering as an attempt to trick a person into revealing information that can be used to attack systems or networks. Phishing is one form of this activity, often using deceptive messages or websites to obtain sensitive information. NIST CSRC: Social Engineering and NIST CSRC: Phishing.
Look at the attacker’s method, the channel used, and the action requested. Voice delivery points toward vishing; text-message delivery points toward smishing; a fabricated story points toward pretexting; and a fraudulent business payment request may indicate business email compromise.
Anatomy of a Social-Engineering Attempt
Many social-engineering incidents follow a recognizable pattern, although real attacks may skip, repeat, or combine steps. The attacker may research a target, build credibility, create pressure, request an action, and then use the result.

Common manipulation signals
“Act Immediately”
The request claims an account will be closed, a payment will fail, or a deadline will be missed unless the target acts immediately.
“The Executive Asked”
The sender claims to be a senior leader, regulator, police officer, or IT administrator to discourage questioning.
“Avoid a Penalty”
A threat, prize, refund, promotion, or reward pushes the recipient toward a decision before checking the facts.
“Keep This Confidential”
The attacker uses a familiar identity, shared context, or secrecy request to bypass normal approval and verification.
1. Phishing, Spear Phishing, and Whaling
Phishing uses deceptive communications to persuade a target to reveal sensitive information, visit a fraudulent destination, download harmful content, or perform another unsafe action. Email is a common delivery channel, but phishing-related deception may also occur through websites and other electronic communications.
| Technique | Targeting approach | Scenario clue |
|---|---|---|
| Phishing | Messages sent to a broad or selected set of potential victims. | A fake service alert asks many users to sign in through a suspicious link. |
| Spear phishing | A tailored attempt aimed at a particular person, team, or organization. | A message references a real project and imitates a known colleague. |
| Whaling | A targeted attack focused on senior or high-value individuals. | A fake legal notice or urgent finance request targets the chief financial officer. |
A phishing message may imitate a cloud provider, bank, delivery company, government service, or internal IT team. Common warning signs include an unexpected attachment, unusual sender address, mismatched link destination, request for credentials, unfamiliar payment details, or pressure to bypass standard procedures.
Phishing describes the deceptive approach; spear phishing emphasizes tailored targeting; and whaling emphasizes high-value or senior targets. An attack can be both highly targeted and directed at an executive.
2. Vishing and Smishing
Vishing
Vishing is phishing conducted through voice calls or voice messages. The caller may impersonate a help desk, bank, supplier, executive, or authority.
- Requests an MFA code or password.
- Demands remote access to a computer.
- Pressures an employee to approve a payment or account change.
Smishing
Smishing is phishing delivered through SMS or text messaging. Messages often imitate delivery alerts, account warnings, payment notices, or multi-factor authentication requests.
- Uses a shortened or unfamiliar link.
- Claims an account is blocked or a parcel is delayed.
- Asks for credentials, payment details, or a verification code.

3. Business Email Compromise (BEC)
Business email compromise (BEC) is a fraud technique that abuses business email communications, impersonated identities, or compromised accounts to influence a financial or sensitive business action. It often targets payment processes, payroll changes, confidential files, or access to business information.
Common BEC scenarios
Executive Impersonation
A message appears to come from a senior leader and asks an employee to make an urgent, confidential transfer outside the normal process.
Supplier Payment Redirection
A fraudulent or compromised email requests a change to the supplier’s bank details shortly before an invoice is paid.
Compromised Mailbox
An attacker uses a legitimately accessed account to send convincing requests from an existing email thread.
Payroll or Tax Fraud
A fake employee or executive request attempts to redirect salary payments or obtain sensitive payroll information.
Independently verify bank-detail changes, urgent transfers, gift-card requests, payroll updates, and requests to bypass normal approvals. Do not rely solely on the display name or the fact that a message appears within a familiar email conversation.
4. Pretexting and Impersonation
Pretexting uses a fabricated story or situation to make a request appear legitimate. Impersonation involves pretending to be a trusted person, role, company, or authority. The two techniques can occur together, but they describe different aspects of a social-engineering attempt.
| Technique | What defines it? | Example |
|---|---|---|
| Pretexting | A fabricated story, context, or reason used to gain confidence or obtain information. | A caller invents an account-verification problem to request an employee’s details. |
| Impersonation | A false identity or role intended to be accepted as genuine. | A person pretends to be an IT technician to request account access. |
| Combined example | A false identity supports a fabricated story. | Someone claiming to be a payroll vendor says a system error requires urgent bank-detail confirmation. |
Pretexting works best when the story matches a real workflow, such as onboarding, payroll, technical support, an audit, or a supplier relationship. Verify the request independently rather than relying on the story’s plausibility.
5. Misinformation and Disinformation
Misinformation
Misinformation is false or inaccurate information spread without necessarily intending to deceive.
Example: an employee forwards an incorrect security warning because they believe it is genuine.
Disinformation
Disinformation is false information deliberately created or spread to mislead a target or audience.
Example: an attacker fabricates a fake internal notice to persuade staff to send credentials to a fraudulent address.
The important distinction is intent: misinformation can be repeated by someone who believes it; disinformation is intentionally deceptive. In real incidents, determining intent may require evidence, so do not assume it from inaccurate content alone.
6. Watering-Hole Attacks
A watering-hole attack targets a website or online resource that members of a particular group are likely to visit. Instead of contacting every target directly, an attacker attempts to compromise or abuse a destination trusted or regularly used by the target community.
Employees in a specialist industry regularly visit the same professional resource. An attacker compromises that website and uses it to expose visitors to harmful content.
Why it fits: the chosen website is a destination used by the intended target group.
Defense: patch browsers and endpoints, filter and monitor web traffic, restrict unnecessary execution, and use layered detection. A familiar website should not automatically be treated as risk-free.
7. Brand Impersonation
Brand impersonation misuses a company’s identity, logo, language, or visual style to make a message, account, advertisement, or website appear genuine. Attackers may imitate a cloud service, financial institution, software vendor, delivery company, or an organization’s own IT team.
A convincing logo is not proof that a communication is authentic. Check the actual sender address, destination domain, expected business context, and requested action. Use trusted bookmarks or official apps for sign-in and payment activity.
8. Typosquatting
Typosquatting uses a domain name that resembles a legitimate domain, often by exploiting a typing error or visual similarity. A look-alike page may imitate the real sign-in screen or ask the user to download a file.
For example, a fraudulent domain might contain an extra character, a transposed letter, or a visually similar character. Do not rely on a site’s branding or padlock symbol alone to determine whether the destination is legitimate.
Brand impersonation emphasizes misuse of a brand’s identity. Typosquatting emphasizes a look-alike domain name. An attacker may use both in the same incident.
9. Social-Engineering Technique Comparison

| Scenario clue | Best-fit technique | What to remember |
|---|---|---|
| Broad deceptive email or online solicitation | Phishing | Deception intended to prompt disclosure or action. |
| Tailored message aimed at a named employee or team | Spear phishing | Target-specific content. |
| Targeted message aimed at a senior leader | Whaling | High-value target. |
| Deceptive call or voice message | Vishing | Voice channel. |
| Deceptive SMS or text | Smishing | Text-message channel. |
| Fraudulent request related to company email or payments | BEC | Business communication or identity abuse for fraud. |
| A made-up story creates a reason for the request | Pretexting | Fabricated context. |
| A false role or identity is used | Impersonation | Pretending to be trusted. |
| A trusted niche website is compromised for a target group | Watering hole | Targeted website destination. |
| A fake notice or website copies a brand | Brand impersonation | Misused brand identity. |
| A look-alike domain exploits spelling errors | Typosquatting | Deceptive domain name. |
| False information spreads without proven intent to deceive | Misinformation | Intentional deception is not required. |
| False information is deliberately spread to mislead | Disinformation | Intentional deception. |
10. How to Respond to a Suspected Social-Engineering Attempt
The goal is to interrupt the attack before it results in credential theft, unauthorized access, payment fraud, data exposure, or malware execution.

Do not click, disclose a code, transfer money, open a suspicious file, or approve an unexpected sign-in simply because the request sounds urgent.
Use a saved contact, trusted directory, known website, or established approval workflow. Do not use contact details supplied only in the suspicious request.
Never share passwords or one-time authentication codes with a caller or sender. Deny unrecognized MFA prompts and follow organizational procedures.
Use the approved reporting mechanism. Preserve message details or call information and follow guidance for handling suspected incidents.
Controls that reduce social-engineering risk
People and Process
- Provide regular, scenario-based security-awareness training.
- Require independent verification for payment and account changes.
- Use separation of duties for high-risk financial actions.
- Maintain a clear reporting channel without discouraging good-faith reports.
- Practice incident reporting and follow-up procedures.
Technical Controls
- Use email filtering and anti-phishing protections.
- Enable phishing-resistant authentication where supported and appropriate.
- Use domain-protection measures such as SPF, DKIM, and DMARC for organizational email.
- Apply endpoint protection, browser safeguards, and least privilege.
- Monitor suspicious account activity and provide a reliable way to report incidents.
Report the incident promptly using the organization’s process. Follow its instructions for securing the account or device, changing affected credentials, revoking sessions or tokens where appropriate, contacting the bank or payment team if funds may be at risk, and preserving evidence. Do not conceal the event or delay reporting out of embarrassment.
11. Common Security+ Exam Traps
- Vishing is voice; smishing is SMS. The channel is a defining clue.
- Pretexting is a fabricated story. Impersonation is a false identity. One attack may involve both.
- BEC is business-focused fraud. It may use spoofed identities or compromised mailboxes, and may not contain an obvious malicious attachment.
- Misinformation does not require deliberate deception. Disinformation is intentionally misleading.
- Watering hole targets a website used by a target group. It is not simply any malicious website.
- Typosquatting involves a look-alike domain. Brand impersonation focuses on deceptive use of brand identity.
- Urgency is not proof of legitimacy. Verify payment changes, credentials requests, and privileged-access requests through independent channels.
- One incident can combine techniques. Choose the most specific technique supported by the question’s wording.
12. Quick Reference
| Fast scenario clue | Answer to consider |
|---|---|
| Fraudulent message tries to obtain sensitive information | Phishing |
| Message is tailored to a specific employee or team | Spear phishing |
| Target is a senior executive or high-value leader | Whaling |
| Fraudulent request is delivered by phone | Vishing |
| Fraudulent request is delivered by text | Smishing |
| Fake executive or supplier request attempts to redirect funds | Business email compromise |
| Invented situation or story builds trust | Pretexting |
| False identity or role is used | Impersonation |
| Website visited by a target group is compromised | Watering hole |
| Brand identity is copied to appear genuine | Brand impersonation |
| Look-alike web address takes advantage of typing mistakes | Typosquatting |
| False information shared without proven deceptive intent | Misinformation |
| False information created or spread deliberately to mislead | Disinformation |
Recognize the attacker’s method and the clue that distinguishes it from similar techniques. Then choose the control that interrupts the request safely: pause, verify independently, protect credentials, and report suspicious activity.
Practice Questions
10 scenario-based review questions. Expand each question to reveal its answer and explanation.
Exam Quiz
Lesson 02.3 — Social Engineering Attacks · 15 questions · 10 minutes
Social Engineering — Exam Simulation
Identify social-engineering methods from realistic scenarios. Questions focus on phishing variants, BEC, pretexting, impersonation, misinformation, disinformation, watering-hole attacks, brand impersonation, and typosquatting.
15 Questions
Lesson 02.3 scope
10 Minutes
Timed attempt
Instant Feedback
Explanation after each answer
Answer Review
Score and explanations
Lesson 02.3 — Summary
Social Engineering Attacks: Phishing, Vishing, Smishing, BEC, and More
Domain 2.0 — Threats, Vulnerabilities and Mitigations · 22% of Security+ SY0-701
📌 Key Takeaways from Lesson 02.3
Spear phishing targets specific people; whaling focuses on high-value targets.
Identify the channel and requested action.
Verify payment, payroll, and supplier changes independently.
Impersonation involves a false identity; one incident can use both.
Disinformation is deliberately deceptive.
Check destinations and identities instead of trusting appearances.
⚡ Exam Tips — Lesson 02.3
- Identify the channel: voice = vishing; SMS = smishing.
- Look for a fabricated story when the likely answer is pretexting.
- Look for payment redirection or business-email fraud when considering BEC.
- Distinguish misinformation from deliberately deceptive disinformation.
- Look for the target group’s frequently visited website in a watering-hole attack.
- Look for a similar-looking domain name in typosquatting.
- Verify unusual requests independently; urgency and branding alone do not prove legitimacy.
⚠️ Common Pitfalls — Lesson 02.3
📋 Complete Security+ SY0-701 Guide Series — 5 Domains · 57 Numbered Lessons
Further Reading and Related Guides
Continue learning on NetworkUstad:
- Security+ Domain 2.0 Guide Hub — browse Domain 2 lessons.
- Security+ SY0-701 Guide Hub — access the full certification series.
External references:
- NIST CSRC: Social Engineering — terminology for human manipulation attacks.
- NIST CSRC: Phishing — phishing terminology and examples.
- CompTIA Security+ SY0-701 Exam Objectives — official objective reference.