- What a vulnerability is and how it differs from a threat, an exploit, and risk.
- How misconfiguration, mobile devices, and zero-day vulnerabilities create exposure.
- How application weaknesses include memory injection, buffer overflow, race conditions, and malicious updates.
- How SQL injection and cross-site scripting affect web applications.
- Why end-of-life systems, firmware, virtualization, cloud configurations, suppliers, and cryptographic implementations require attention.
- How to classify vulnerability scenarios and choose an appropriate mitigation direction.
This lesson covers CompTIA Security+ objective 2.3: Explain various types of vulnerabilities. It focuses on recognizing the weakness and its environment; enterprise mitigation techniques will be developed further in the mitigation lessons.
What Is a Security Vulnerability?
A security vulnerability is a weakness in software, hardware, configuration, process, or system design that could be exploited or otherwise lead to a security impact. A weakness does not necessarily mean that an attack has already occurred. It indicates an opportunity for harm if the conditions and access requirements allow it.
Vulnerabilities can arise from coding mistakes, unsafe default settings, missing updates, weak access controls, insecure cloud permissions, faulty firmware, unsupported systems, or weaknesses in a third-party component. Some are technical flaws; others result from how a system has been deployed, maintained, or connected.
Vulnerability: a weakness that may be exploited.
Threat: a circumstance or actor that could cause harm.
Exploit: a method or code that takes advantage of a weakness.
Risk: the potential for loss or harm, considering factors such as likelihood and impact.
| Situation | Best-fit concept | Why |
|---|---|---|
| A server uses an unsafe access-control setting. | Vulnerability | The configuration creates a weakness. |
| An attacker wants to access the exposed server. | Threat actor or threat | The attacker or harmful possibility is the threat. |
| A crafted request takes advantage of a flaw. | Exploit activity | The request is used to trigger the weakness. |
| The server holds sensitive customer records and is exposed to the internet. | Risk context | Exposure and the consequences of compromise help determine risk. |
How Vulnerability Assessment Fits Together
Security teams typically discover assets, identify potential weaknesses, validate findings, assess business impact, prioritize remediation, and verify the result. The precise workflow varies by organization, system, and assessment method.

A scan may report a possible weakness, but the analyst still needs to consider the asset’s configuration, software version, exposure, compensating controls, and business importance. Findings should be prioritized rather than treated as equally urgent.
1. Misconfiguration
A misconfiguration occurs when a system, application, account, service, or security control is set up in an unsafe or unintended way. The software itself may be functioning as designed, yet its configuration creates unnecessary exposure.
Configuration Weaknesses
- Cloud storage allows public access when it should be private.
- A firewall rule exposes an administrative service to an untrusted network.
- A database account has excessive privileges.
- Debugging features or sample applications remain enabled in production.
- Security logging or required protections are disabled.
Unsafe Settings
Scenario wording often mentions a permission, setting, rule, policy, or deployment choice that does not meet the intended security requirement.
Misconfigurations can affect confidentiality, integrity, or availability. For example, public access to a private storage bucket may expose data, while an overly broad firewall rule may permit unauthorized connections.
2. Mobile-Device Vulnerabilities: Sideloading and Jailbreaking
Sideloading
Sideloading means installing an application through a route outside the platform’s usual approved app-distribution process. Sideloading is not automatically malicious in every environment, but it can increase risk when apps are obtained from untrusted sources or bypass normal review and security controls.
Jailbreaking
Jailbreaking refers to bypassing platform restrictions on a device, commonly associated with Apple mobile devices. Related rooting activity on Android devices can also weaken the platform’s expected security boundaries. The resulting risk depends on what protections were changed, which apps run, and how the device is managed.
Sideloading is about the application installation route. Jailbreaking is about bypassing operating-system or device restrictions. They are different concepts, although a device may experience both.
Organizations can reduce mobile risk through approved app sources, mobile device management, application policies, timely updates, device integrity checks, and restrictions on access from devices that do not meet security requirements.
3. Zero-Day Vulnerabilities
A zero-day vulnerability is a software or system weakness for which the affected vendor has had no opportunity to provide a fix before the weakness becomes known or exploited. The exact term is used in different contexts, but the exam-relevant idea is that a conventional vendor patch may not yet be available when the weakness is being exploited.
A newly discovered browser flaw is being exploited. The vendor has confirmed the issue but has not released a security update.
Why it fits: defenders cannot rely on an already available vendor patch for the newly discovered flaw.
Possible response: apply vendor-recommended workarounds, restrict exposure, use available detection and prevention controls, monitor advisories, and deploy the verified fix as soon as it becomes available.
Do not confuse a zero-day with every unpatched vulnerability. An older, publicly documented weakness may have a vendor patch available, even when an organization has not installed it. In that case, the issue is generally an unpatched vulnerability rather than necessarily a zero-day.
4. Application Vulnerabilities
Application vulnerabilities occur when software logic, memory handling, input processing, update mechanisms, or interactions between operations create a weakness. The underlying cause matters because similar symptoms can require different fixes.
Memory Injection
Memory injection refers to introducing or manipulating code or data in a program’s memory in a way that can alter execution or enable unauthorized activity. The exact technique depends on the application and operating environment.
Buffer Overflow
A buffer overflow occurs when software writes more data to a buffer than the allocated space can safely hold. Depending on the context, this can corrupt memory, crash a program, or enable further exploitation.
Race Conditions
A race condition occurs when a result depends on the timing or order of concurrent operations in a way that produces an unsafe state. A time-of-check to time-of-use (TOCTOU) problem is a specific pattern.
Malicious Updates
An update can become a threat when an attacker compromises the delivery process, signing material, vendor environment, or distribution channel, or when the update itself is malicious.
Time-of-Check to Time-of-Use (TOCTOU)
In a TOCTOU race condition, an application checks whether a resource is safe or permitted, but the relevant state changes before the application uses that resource. If the application relies on the earlier check without safely protecting the interval, an attacker may exploit the gap.
The application verifies a file, resource, or permission.
The resource or relevant state changes before use.
The application acts on the resource based on an outdated assumption.
An unsafe operation may occur depending on permissions and implementation.
5. Web Vulnerabilities: SQL Injection and Cross-Site Scripting
SQL Injection (SQLi)
SQL injection occurs when an application handles untrusted input in a way that allows it to interfere with database queries. Depending on the application’s privileges and database design, this can expose records or change database behavior.
A web application’s search or login function constructs database commands unsafely from user input. The input changes the meaning of the query instead of being treated only as data.
Best-fit concept: SQL injection.
Defensive direction: parameterized queries, safe database APIs, least-privilege database accounts, input handling, and security testing.
Cross-Site Scripting (XSS)
Cross-site scripting (XSS) occurs when an application allows untrusted content to execute as script in another user’s browser. Depending on context and impact, it can enable actions such as manipulating page content or targeting data available to the vulnerable site.
A web application displays untrusted content without suitable context-aware output encoding. The browser interprets the content as executable script.
Best-fit concept: cross-site scripting.
Defensive direction: context-aware output encoding, safe templating, input validation where appropriate, and additional browser security controls.
| Feature | SQL Injection | Cross-Site Scripting |
|---|---|---|
| Primary target | Database query construction and execution. | Script execution in a user’s browser in the context of a web application. |
| Typical weakness | Unsafe construction of database queries from untrusted input. | Unsafe handling or rendering of untrusted content. |
| Core defensive idea | Parameterized queries and least-privilege database access. | Context-aware output encoding and safe rendering. |
| Scenario clue | Input changes database-query behavior. | Untrusted content runs as script in the browser. |
6. Operating-System, Hardware, Firmware, End-of-Life, and Legacy Vulnerabilities
Vulnerabilities can exist in operating systems, device hardware, and firmware. The operating system may contain a software flaw; firmware may have insecure implementation or outdated code; and hardware-related weaknesses may arise from design or implementation characteristics.
Operating-System Vulnerabilities
OS weaknesses may affect privileges, isolation, authentication, memory handling, system services, or security boundaries. Applying supported security updates and enforcing secure configurations helps reduce exposure.
Hardware and Firmware
Firmware runs close to the hardware and controls important device functions. Weak firmware, insecure boot design, or unavailable updates may undermine device security even when application software is patched.
End-of-Life (EOL)
An EOL product has reached the end of its defined lifecycle or support. Depending on the vendor’s policy, security updates or support may no longer be provided.
Legacy Systems
Legacy systems are older systems retained because of business or technical dependencies. They may be difficult to upgrade, integrate, monitor, or protect with modern controls.
Exam distinction: EOL is a lifecycle or support status; legacy describes an older system that remains in use. A legacy system may still be supported, and a product at EOL may be relatively recent. What matters is the actual support status and the security exposure.
7. Virtualization Vulnerabilities
Virtual Machine (VM) Escape
A VM escape occurs when code or activity inside a virtual machine crosses an intended isolation boundary to interact with the host or another protected part of the virtualization environment. This is serious because virtualization depends on isolation between guest workloads and underlying resources.
Resource Reuse
Resource reuse risk can arise when storage, memory, or another resource is reassigned without sufficiently clearing or isolating residual data or state from a previous user or workload.
If a guest VM affects the hypervisor or escapes its isolation boundary, consider VM escape. If one workload can access residual information or state left by another because a reused resource was not properly sanitized or isolated, consider resource reuse.
8. Cloud-Specific Vulnerabilities
Cloud deployments can introduce weaknesses through unsafe identity permissions, publicly exposed storage, overly permissive network rules, insecure APIs, weak secret handling, misconfigured logging, or misunderstood shared-responsibility boundaries.
| Example | Potential weakness | Security consideration |
|---|---|---|
| A storage resource is unintentionally public. | Exposure of sensitive data. | Review access policy, public-access settings, and data classification. |
| A cloud identity has broad permissions it does not need. | Excessive privilege. | Apply least privilege, review roles, and monitor privileged activity. |
| An API accepts requests without sufficient authorization. | Unauthorized access to application functions or data. | Enforce server-side authorization, secure tokens, and test access boundaries. |
| Secrets are embedded in code or openly stored. | Credential or key exposure. | Use controlled secret storage, restrict access, and rotate affected secrets. |
| Cloud logging is incomplete or not monitored. | Reduced ability to detect and investigate activity. | Enable the required logs, protect them, and verify monitoring coverage. |
Cloud responsibility is divided between the provider and customer according to the service model and contract. Moving a workload to cloud infrastructure does not automatically fix application flaws, identity mistakes, unsafe data exposure, or poor operational processes.
9. Supply-Chain Vulnerabilities
A supply-chain vulnerability may originate from a service provider, hardware provider, software provider, or another dependency in the delivery and maintenance chain. An organization may inherit exposure through a product, update, dependency, outsourced process, or third-party access path.
Third-Party Services
A provider’s remote access, operational process, or service configuration may introduce risk to customer environments.
Hardware Supply
Hardware components, firmware, manufacturing, or support channels may contain weaknesses or be compromised.
Software and Updates
A vulnerable dependency, malicious package, compromised update process, or insecure development practice may affect downstream users.
Supplier and service-provider risk can be reduced through appropriate due diligence, access restrictions, software and asset inventories, update verification, contract requirements, monitoring, and clear incident-notification procedures.
10. Cryptographic Vulnerabilities
Cryptographic vulnerabilities arise when security depends on a weak algorithm, incorrect implementation, poor key management, inappropriate protocol settings, or unsafe use of otherwise sound cryptographic tools.
Weak or Obsolete Algorithms
An outdated or insufficient algorithm may no longer provide the intended level of protection. Organizations should follow current security guidance and supported configurations.
Poor Key Management
Exposed, reused, weakly protected, or poorly rotated keys can undermine encryption even when the underlying algorithm is strong.
Incorrect Implementation
Unsafe parameter choices, incorrect protocol negotiation, or mistakes in cryptographic code can weaken otherwise sound designs.
Unsafe Configuration
Allowing obsolete protocol versions or weak cipher options can downgrade the security offered by a connection.
Do not assume that encryption alone makes an application secure. The overall result depends on algorithm choice, implementation, keys, protocol configuration, endpoint security, and access control.
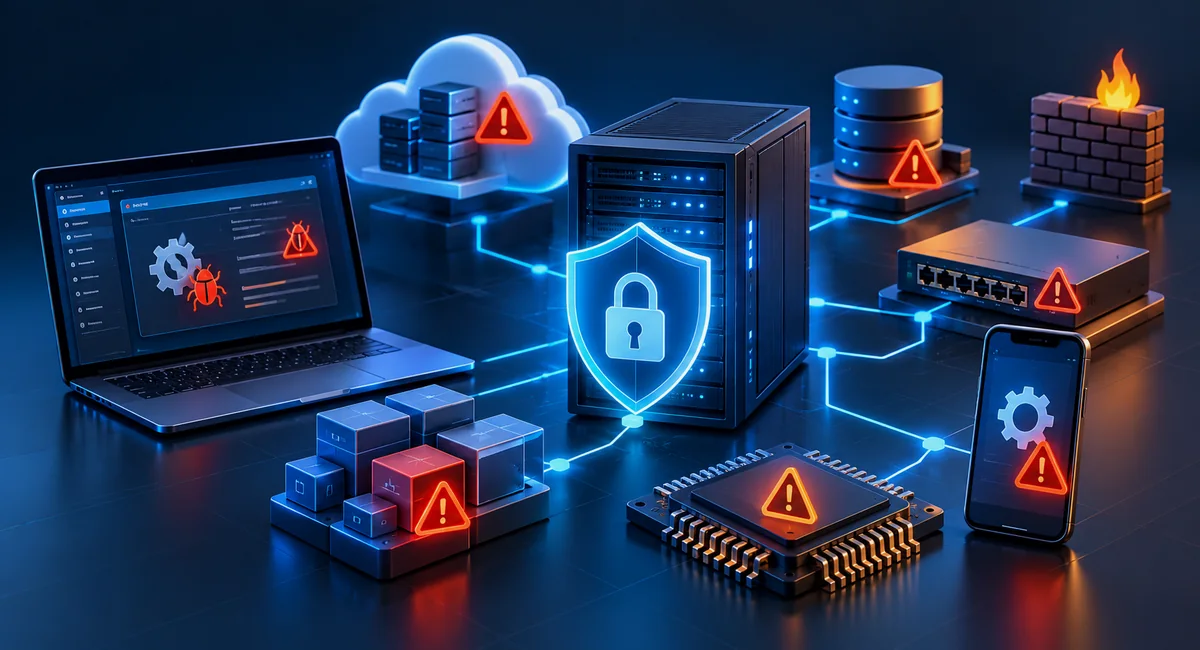
11. Vulnerability Types — Visual Reference

12. How to Classify a Vulnerability Scenario

Look for words describing unsafe settings, software flaws, memory handling, timing, device restrictions, old systems, or third-party components.
Match the weakness to misconfiguration, application, web, mobile, OS, hardware, virtualization, cloud, supply-chain, or cryptographic vulnerability.
Determine what resource, data, process, identity, or isolation boundary is affected.
Consider secure configuration, patching, upgrades, isolation, access restrictions, safe coding, or a vendor-recommended workaround.
Common Security+ Exam Traps
- Misconfiguration is not necessarily a code flaw. The product may work as designed while its settings expose the system.
- Zero-day does not mean every unpatched flaw. It usually describes a weakness with no available vendor fix when it is discovered or exploited.
- Buffer overflow is a memory-handling issue. SQL injection is about unsafe database-query construction; XSS is about script execution in a user’s browser.
- TOCTOU is a race-condition pattern. The relevant state changes between a security check and use.
- EOL and legacy are not identical. EOL is a support or lifecycle status; legacy describes an older system that remains in use.
- VM escape crosses a virtualization isolation boundary. Resource reuse concerns residual state or data when resources are reassigned.
- Cloud and supply-chain weaknesses remain security concerns. Hosted infrastructure and trusted vendors do not automatically remove customer responsibility.
- Cryptographic strength depends on implementation and key handling too. Strong algorithms can be undermined by weak configuration or exposed keys.
Quick Reference
| Scenario clue | Vulnerability category |
|---|---|
| Unsafe permissions, exposed storage, or risky system settings | Misconfiguration |
| Application installed outside approved distribution or platform restrictions bypassed | Sideloading or jailbreaking |
| Newly exploited flaw with no vendor fix available yet | Zero-day vulnerability |
| Program writes beyond allocated buffer space | Buffer overflow |
| Program checks a resource and the state changes before use | TOCTOU race condition |
| Untrusted input changes a database query | SQL injection |
| Untrusted content executes as script in a browser | Cross-site scripting (XSS) |
| Unsupported operating system, firmware, or older component | OS, firmware, EOL, or legacy vulnerability |
| Guest VM crosses the intended isolation boundary | VM escape |
| Public cloud storage or excessive cloud permissions | Cloud-specific vulnerability or misconfiguration |
| Compromised provider, component, dependency, or update source | Supply-chain vulnerability |
| Weak algorithm, unsafe cryptographic implementation, or exposed keys | Cryptographic vulnerability |
Find the specific weakness described, classify its environment, and avoid confusing a vulnerability with the actor, attack method, or resulting impact. Then consider the most appropriate mitigation for that weakness.
Practice Questions
10 scenario-based review questions. Expand any question to reveal the answer and explanation.
Exam Quiz
Lesson 02.4 — Vulnerability Fundamentals · 15 questions · 10 minutes
Vulnerability Types — Exam Simulation
Identify misconfiguration, mobile, zero-day, application, web, operating-system, hardware, virtualization, cloud, supply-chain, and cryptographic vulnerabilities.
15 Questions
Lesson 02.4 scope
10 Minutes
Timed attempt
Instant Feedback
Explanation after each answer
Answer Review
Score and explanations
Lesson 02.4 — Summary
Vulnerability Fundamentals: Misconfigurations, Zero-Day Flaws, and More
Domain 2.0 — Threats, Vulnerabilities and Mitigations · 22% of Security+ SY0-701
📌 Key Takeaways from Lesson 02.4
Review access, permissions, network rules, and cloud configurations.
Buffer overflow, race conditions, SQLi, and XSS are not interchangeable.
Sideloading, jailbreaking, and zero-day vulnerabilities describe different problems.
Unsupported systems and isolation failures can create significant risk.
Review providers, permissions, updates, components, and third-party access.
Strong algorithms can be undermined by weak settings or exposed keys.
⚡ Exam Tips — Lesson 02.4
- Classify the exact weakness before choosing a response.
- Remember: SQLi targets query handling; XSS involves script execution in a browser.
- Look for the check-use timing gap in a TOCTOU scenario.
- Distinguish zero-day weaknesses from older flaws that already have available patches.
- Recognize VM escape as a virtualization isolation-boundary problem.
- Consider configuration, identity permissions, key management, and supplier dependencies—not only software code.
⚠️ Common Pitfalls — Lesson 02.4
📋 Complete Security+ SY0-701 Guide Series — 5 Domains
Further Reading and Related Guides
Continue learning on NetworkUstad:
- Security+ Domain 2.0 Guide Hub — browse the Domain 2 lesson sequence.
- Security+ SY0-701 Guide Hub — access the complete certification guide series.
External references:
- CompTIA — official certification and exam resources.
- NIST CSRC Glossary — security terminology and definitions.
- OWASP Top 10 — web application security risk reference.