API Security Best Practices for Fintech in 2026: What Generic Checklists Miss
Most API security checklists focus solely on OAuth, TLS, rate limiting, and web application firewalls. While…
From zero-day breakdowns to enterprise hardening guides — expert security content built for practitioners, not just beginners.
Every major domain of modern cybersecurity — from network defense to threat intelligence to compliance.
Firewalls, IDS/IPS, Zero Trust architecture, micro-segmentation, and perimeter defense strategies.
APT group tracking, CVE deep dives, malware analysis, and real-world attack campaign breakdowns.
TLS/mTLS, certificate lifecycle management, post-quantum migration, and key infrastructure design.
Methodology, red team techniques, tooling (Nmap, Metasploit, Burp Suite), and responsible disclosure.
AWS/Azure/GCP hardening, IAM design, CSPM, container security, and serverless threat models.
Zero Trust identity, MFA, PAM, SSO federation, and least-privilege access design.
IR playbooks, digital forensics, SIEM, log analysis, and post-breach recovery guides.
ISO 27001, NIST CSF, SOC 2, GDPR implementation, and security program management.
Fresh analysis, guides, and threat breakdowns.
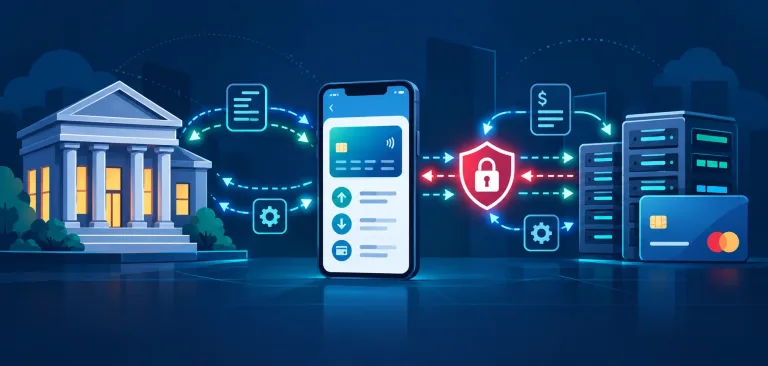
Most API security checklists focus solely on OAuth, TLS, rate limiting, and web application firewalls. While…
If you’ve come across “Proxy Orb” (branded as ProxyOrb) while looking into ways to access a…
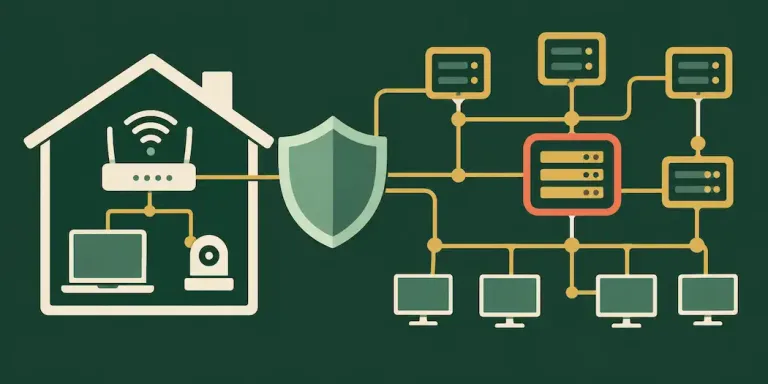
“Keep my network safe” is one of those searches that means something slightly different depending on…