Search Results
Showing results for "business" (3640 articles found)
Setting Up a Limited Liability Company in Slovenia: A Step-by-Step Overview for Foreign Founders
Slovenia’s most common company form for foreign entrepreneurs is the limited liability company, known locally as a d.o.o. Non-EU citizens without Slovenian residency can found one, and so can foreign legal entities. If you are weighing it, this is what the process looks like in practice. The capital requirement Founders must provide minimum share capital...
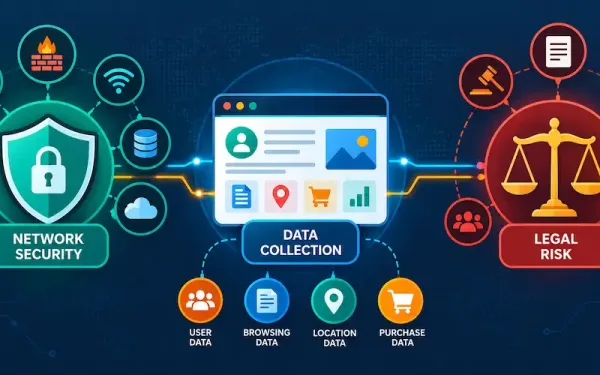
Build vs Buy? The Network, Security and Legal Considerations of Social Media Data Collection
It usually starts as a small ticket. “We want competitor posts in our dashboard.” Or “Get us Reddit threads for the sentiment model.” Or maybe someone has read about an AI agent that can just look things up on LinkedIn. It looks like a bit of code and a cron job. It won’t be that...
Mitigation Techniques and Security Controls: Hardening, Patching, Segmentation, and More
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.6 Mitigation Techniques and Security Controls: Hardening, Patching, Segmentation, and More WHAT YOU’LL LEARN How mitigation techniques reduce the likelihood and impact of security incidents. How network segmentation and isolation limit attacker movement. How access control, ACLs, permissions, and least privilege protect resources. How application allowlisting, patching,...
Indicators of Malicious Activity: Malware, Network, Password, and Application Attacks
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.5 Indicators of Malicious Activity — Recognizing Attack Evidence WHAT YOU’LL LEARN How indicators of malicious activity help analysts recognize suspicious behavior. How to distinguish ransomware, Trojans, worms, spyware, viruses, keyloggers, logic bombs, rootkits, and bloatware. How physical, network, application, cryptographic, and password attacks appear in scenarios....
Vulnerability Fundamentals: Misconfigurations, Zero-Day Flaws, and More
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.4 Vulnerability Fundamentals — Misconfigurations, Zero-Day Flaws, and More WHAT YOU’LL LEARN What a vulnerability is and how it differs from a threat, an exploit, and risk. How misconfiguration, mobile devices, and zero-day vulnerabilities create exposure. How application weaknesses include memory injection, buffer overflow, race conditions, and...
Social Engineering Attacks: Phishing, Vishing, Smishing, BEC, and More
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.3 Social Engineering Attacks — Phishing, Vishing, Smishing, BEC, and More WHAT YOU’LL LEARN How social engineering manipulates trust, urgency, authority, fear, curiosity, or helpfulness. How to distinguish phishing, spear phishing, whaling, vishing, and smishing. How business email compromise, impersonation, and pretexting work in real-world scenarios. How...
Best 7 Agentic AI Companies for Revenue Cycle Management (2026)
Most revenue cycle teams already have automation. Bots log into portals, scripts move data between fields, clearinghouses scrub claims. The work that still lands on people is the exceptions: a benefit check the payer answers only by phone, a prior authorization packet missing one document, a denial that needs a judgment call. That is the...
Threat Vectors and Attack Surfaces: Common Entry Points Explained
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.2 Threat Vectors and Attack Surfaces — Common Entry Points Explained WHAT YOU’LL LEARN How a threat vector differs from an attack surface and a vulnerability. How messages, images, files, voice calls, and removable devices can expose users and systems to threats. Why vulnerable or unsupported software,...
Threat Actors and Motivations: Types, Capabilities, and Attack Goals
COMPTIA SECURITY+ SY0-701 · DOMAIN 2.0 · LESSON 02.1 Threat Actors and Motivations — Types, Attributes, and Attack Goals WHAT YOU’LL LEARN How to distinguish common threat actor types, including nation-state actors, organized crime, hacktivists, insiders, unskilled attackers, and competitors. How internal or external access, resources and funding, and sophistication or capability help compare threat...
Security Frameworks Overview: NIST, ISO 27001, CIS Controls Compared
COMPTIA SECURITY+ SY0-701 · DOMAIN 1.0 · SUPPLEMENTAL GUIDE Security Frameworks Overview · NIST, ISO/IEC 27001, and CIS Controls Compared WHAT YOU'LL LEARN What cybersecurity frameworks, management-system standards, and prioritized control sets are designed to do. How NIST Cybersecurity Framework (CSF) 2.0 organizes cybersecurity risk outcomes. How ISO/IEC 27001:2022 defines requirements for an Information Security...