- What Zero Trust Architecture (ZTA) means and why network location alone is not enough to establish trust.
- The three principles: verify explicitly, use least privilege, and assume breach.
- How identity, MFA, device posture, context, and policy decisions work together.
- The roles of the Policy Engine, Policy Administrator, and Policy Enforcement Point.
- How microsegmentation and continuous monitoring can limit unauthorized access and lateral movement.
- How to recognize Zero Trust controls in Security+ SY0-701 scenarios.
What Is Zero Trust Architecture?
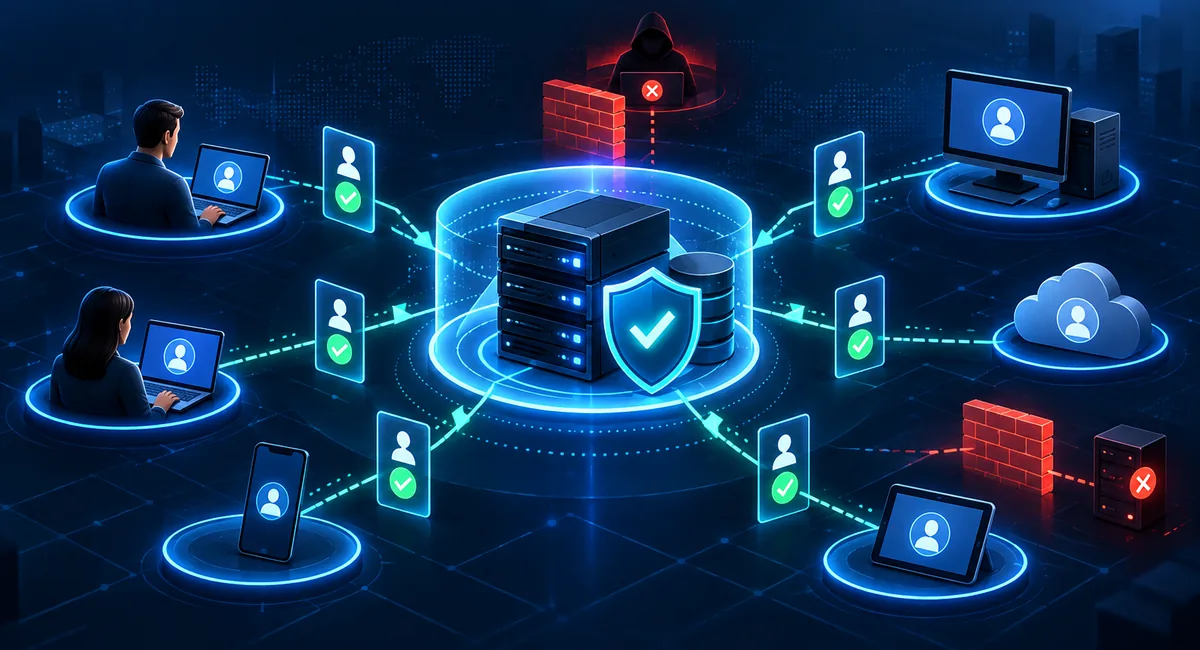
Zero Trust Architecture (ZTA) is a cybersecurity approach that avoids granting implicit trust to users, devices, applications, or services simply because they are inside a corporate network or owned by an organization. Access is evaluated using identity, device state, the requested resource, policy, and available risk signals.
The central idea is simple: never trust a request automatically; verify it and authorize only the access that is needed. Zero Trust focuses security decisions on individual resources and access requests instead of relying only on a trusted internal network perimeter.
Zero Trust does not mean that nobody can ever be trusted. It means trust is not assumed from network location, ownership, or a previous successful login. Access decisions should be explicit, limited, and subject to reassessment.
Why Traditional Perimeter Security Is Not Enough
Traditional security often places strong controls at the network edge, such as firewalls and remote-access gateways. Those controls remain useful, but an internal network is not automatically safe. An attacker may steal an employee's credentials, compromise a device, exploit a vulnerable server, or move laterally after gaining an initial foothold.
Modern organizations also use cloud services, remote workers, mobile devices, contractors, and applications hosted across different environments. A user's physical location may say little about whether a specific request is legitimate.
Inside Means Trusted
Some systems may permit broad access based on network placement once a user or device enters the internal network.
Evaluate Each Request
Identity, device health, resource sensitivity, permissions, and current risk signals inform access decisions.
The Three Core Zero Trust Principles
Verify Explicitly
Authenticate and authorize using relevant evidence, such as user identity, MFA, device posture, the requested resource, and risk context.
Use Least Privilege
Grant only the permissions needed for the task, for the appropriate scope and duration. Avoid unnecessary standing privileges.
Assume Breach
Design controls with the expectation that an account, device, or workload could be compromised. Limit exposure and detect suspicious activity.

Verify Explicitly: Identity, MFA, and Context
Zero Trust decisions should be based on multiple relevant signals rather than one static indicator. Depending on the system, those signals can include:
- User identity: who is requesting access and whether the account is active and authorized.
- Authentication strength: whether multifactor authentication (MFA) or another required method was completed.
- Device posture: whether the endpoint is managed, patched, encrypted, and compliant with policy.
- Requested resource: how sensitive the application, data, or service is.
- Context and risk: signals such as unusual activity, sign-in patterns, time, or approved network conditions.
- Authorization: whether the authenticated user or service has permission to perform the specific action.
Authentication answers, “Who are you?” Authorization answers, “What are you allowed to do?” Zero Trust uses both, and the decision can also depend on device state and contextual risk.
Least Privilege and Just-in-Time Access
Least privilege means a subject receives only the permissions required to perform an approved task. It reduces the potential damage caused by mistakes, compromised credentials, malware, or insider misuse.
Organizations can strengthen least privilege with controls such as role-based access control (RBAC), privileged access management (PAM), just-in-time (JIT) access, time-limited approvals, and separate administrative accounts.
Just-in-Time (JIT) Access
Elevated privileges are granted only when needed and often only for a limited period.
Just Enough Access
Permissions are limited to the specific systems, actions, or data required for the task.
Core Logical Components of Zero Trust Architecture
NIST SP 800-207 describes logical components that help organizations make and enforce resource-access decisions. Implementations differ, but three terms are especially useful for exam questions.
Policy Engine
Makes the access decision by evaluating policy and available information about the request.
Policy Administrator
Implements the decision by establishing or terminating the access path through the enforcement system.
Policy Enforcement Point
Enables, monitors, and can terminate the connection between a subject and a protected resource according to policy.
The Policy Engine decides, the Policy Administrator carries out the decision, and the Policy Enforcement Point controls the access path to the resource.
How a Zero Trust Access Request Works
A typical access request can be understood as a sequence of checks. Real deployments may perform some steps in parallel or reassess them throughout a session.
- A user or service requests a particular resource.
- The system verifies identity and performs the required authentication, which may include MFA.
- The organization evaluates device posture, the requested action, permissions, and available risk signals.
- The policy decision is made. The request is allowed, denied, or challenged for additional verification.
- If approved, access is restricted to the permitted resource and actions.
- Monitoring continues, and access can be adjusted or terminated when conditions change.

Microsegmentation and Limiting Lateral Movement
Microsegmentation divides an environment into small, controlled security zones or workloads and applies more granular rules between them. Instead of permitting broad communication simply because systems share a network, policies restrict which users, devices, applications, or services can communicate.
If one workstation is compromised, microsegmentation can help prevent an attacker from moving freely to file servers, administrative systems, databases, or other sensitive workloads. It is one useful tool for implementing Zero Trust, but it does not replace identity verification or access policy.
Unrestricted Lateral Movement
Systems may have unnecessary east-west connectivity, giving an attacker more opportunities after compromising one host.
Controlled Communication
Only explicitly permitted connections are allowed between zones, applications, or workloads.
Continuous Monitoring and Reassessment
Zero Trust is not a one-time login check. The organization monitors relevant signals and can reassess access when risk changes. Examples include a device becoming noncompliant, an account showing unusual behavior, a session requesting a sensitive operation, or a security alert indicating possible compromise.
Possible responses include requiring reauthentication, reducing privileges, blocking a specific action, isolating a device, or terminating a session. The precise response depends on the organization's policies, technology, and operational requirements.
Zero Trust vs. Traditional Perimeter Security
| Area | Traditional Perimeter Emphasis | Zero Trust Emphasis |
|---|---|---|
| Trust basis | May rely heavily on network location | No implicit trust based solely on location or ownership |
| Access scope | May allow broad internal connectivity | Per-resource, least-privilege authorization |
| Identity | Often validated at initial network entry | Identity is central to resource access decisions |
| Device state | May receive less attention after network access | Device posture can inform policy decisions |
| Monitoring | Can emphasize the network boundary | Uses telemetry and reassessment across sessions and resources |
| Segmentation | Often larger network zones | Can use granular segmentation and workload-level policies |
Important: Zero Trust does not mean removing firewalls, VPNs, or other perimeter controls. These can remain useful; they simply should not be the sole basis for trust.
Practical Steps Toward a Zero Trust Model
Inventory sensitive data, applications, services, devices, and accounts.
Improve authentication, MFA, lifecycle management, and account hygiene.
Monitor endpoint management, patching, encryption, and compliance status.
Remove excessive permissions and use time-bound privileged access where appropriate.
Restrict unnecessary traffic between networks, applications, and workloads.
Collect useful telemetry, detect anomalies, and continuously refine policy.
Real-World Scenario: An Employee Accesses a Cloud File
Scenario
An employee signs in from a company laptop and requests access to a confidential finance folder. Although the laptop is on the corporate network, the access system does not automatically approve the request.
The system verifies the user's identity, checks MFA, evaluates whether the laptop meets device policy, and confirms that the employee's role permits access to the folder. It grants only the approved permissions. If the device later becomes noncompliant or activity becomes suspicious, the organization can require another check or terminate access.
Security lesson: Being on the internal network is not sufficient. Access depends on identity, device and request context, authorization, and ongoing policy enforcement.
Common Zero Trust Misconceptions
Security+ SY0-701 Exam Strategy
Do not choose “allow” merely because a request comes from an internal IP address or a corporate-owned device. Zero Trust evaluates the request with applicable identity, authorization, device, resource, and risk information.
Practice Questions
10 scenario-based questions. Expand each card to reveal the answer and explanation.
Exam Quiz
Lesson 01.5 — Zero Trust Architecture · 15 questions · 10 minutes
Zero Trust — Exam Simulation
Test your understanding of Zero Trust principles, logical components, least privilege, microsegmentation, and continuous monitoring.
15 Questions
Lesson 01.5 scope
10 Minutes
Timed simulation
Instant Feedback
Explanation per answer
Answer Review
Score and corrections
Lesson 01.5 — Summary
Zero Trust Architecture: Never Trust, Always Verify · Domain 1.0 — General Security Concepts · Exam domain weight: 12%
Key Takeaways
| Concept | Purpose | Exam Clue |
|---|---|---|
| Verify Explicitly | Evaluate identity and relevant request context | Authenticate and authorize using multiple signals |
| Least Privilege | Limit permissions, scope, and duration | Only required access |
| Assume Breach | Limit impact and detect compromise | Containment and monitoring |
| Policy Engine (PE) | Evaluates policy and makes the access decision | Decision component |
| Policy Administrator (PA) | Implements the decision and manages the access path | Implements the decision |
| Policy Enforcement Point (PEP) | Controls access to a resource | Enforcement component |
| Microsegmentation | Restricts communications between workloads | Limits lateral movement |
| Continuous Monitoring | Detects changing risk and device posture | Reassess or terminate access |
Exam Tips — Lesson 01.5
- Network location alone does not establish trust.
- MFA supports authentication but does not replace authorization or least privilege.
- Microsegmentation helps limit lateral movement after a compromise.
- PE decides; PA implements; PEP enforces the access path.
- Zero Trust is an architecture and strategy, not a single product.
- Firewalls and VPNs can still support security, but they are not sufficient as the sole basis for trust.
Common Pitfalls
Security+ SY0-701 — Exam Domains
Security Frameworks is a supplemental guide, not a numbered lesson in this sequence.